LOST Project: FORENSIC
This project develops a practical Digital Forensics Environment designed to complement the LOST educational platform, allowing students to learn how cybersecurity incidents are investigated using techniques commonly applied in real-world scenarios. The project combines theoretical content covering digital evidence, chain of custody, legislation, forensic tools, and investigative methodologies with a fully functional hands-on laboratory.
As part of the project, a virtual infrastructure consisting of several Windows and Linux systems was created, where participants take on the role of digital forensic analysts. Through a series of progressively challenging exercises which include collecting evidences, metadata analysis, memory dump examination, disk image inspection and recover hidden information using professional tools such as Autopsy, Volatility, FTK Imager, Wireshark, and Kali Linux.
The ultimate goal is to recreate a realistic digital investigation, demonstrating how activities performed on a system leave traces that can be identified, analyzed, and used as evidence to reconstruct events and establish responsibility.
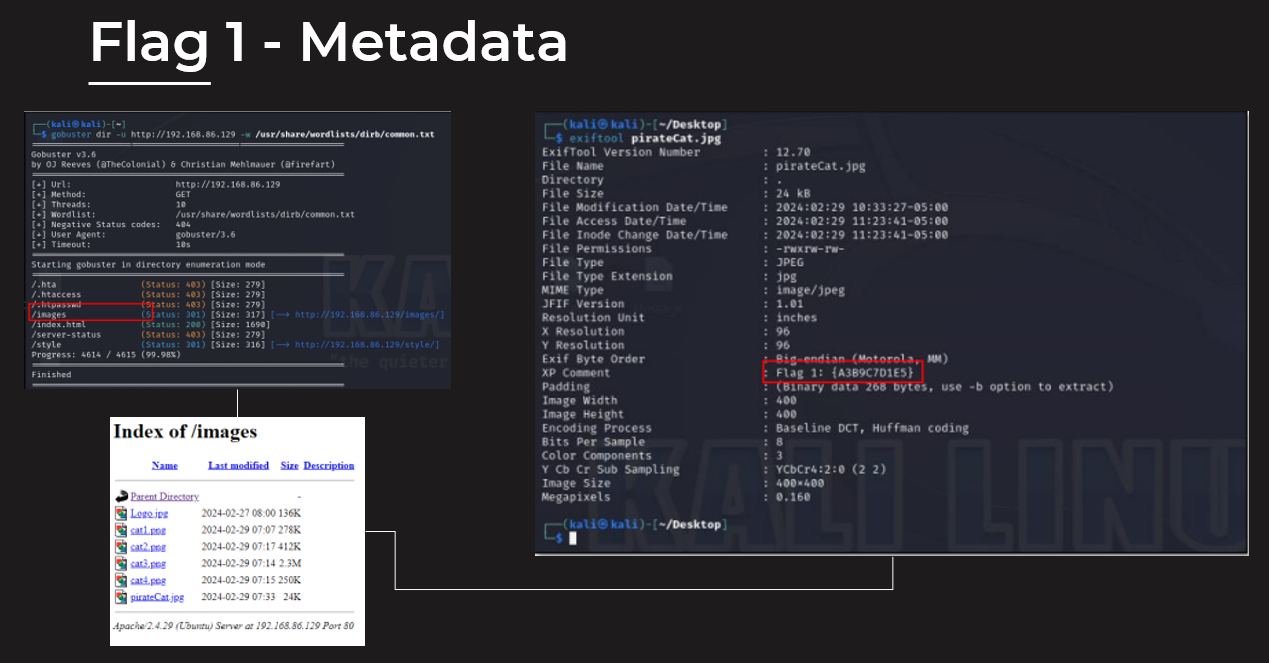
Metadata Analysis using exiftool
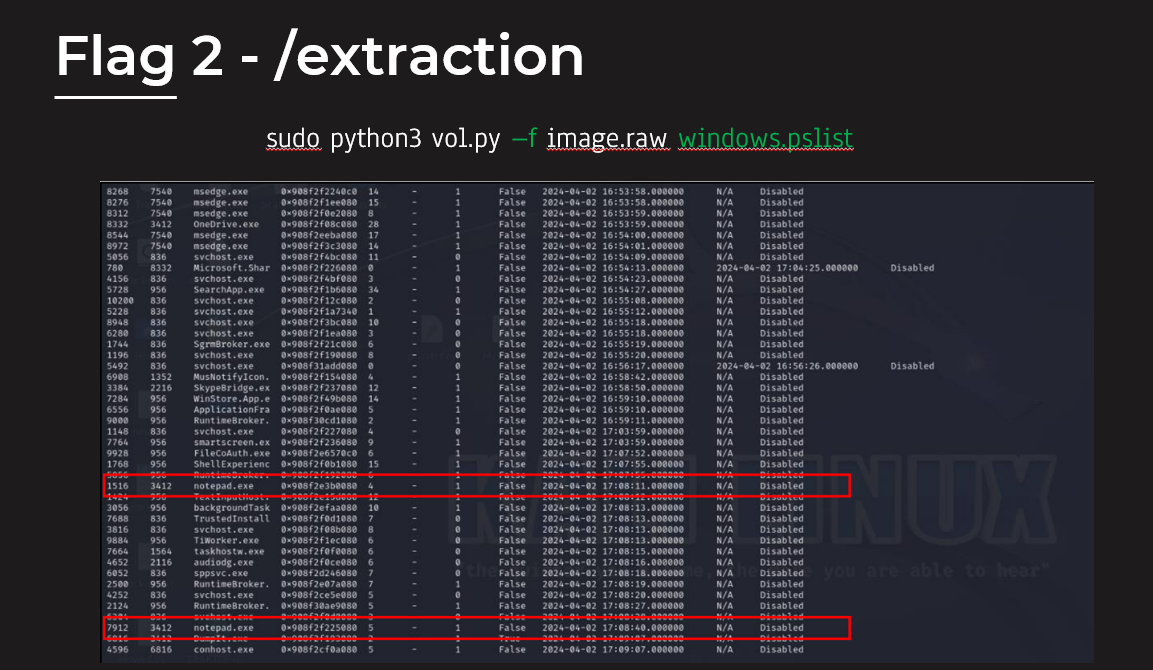
Memory analysis using volatility
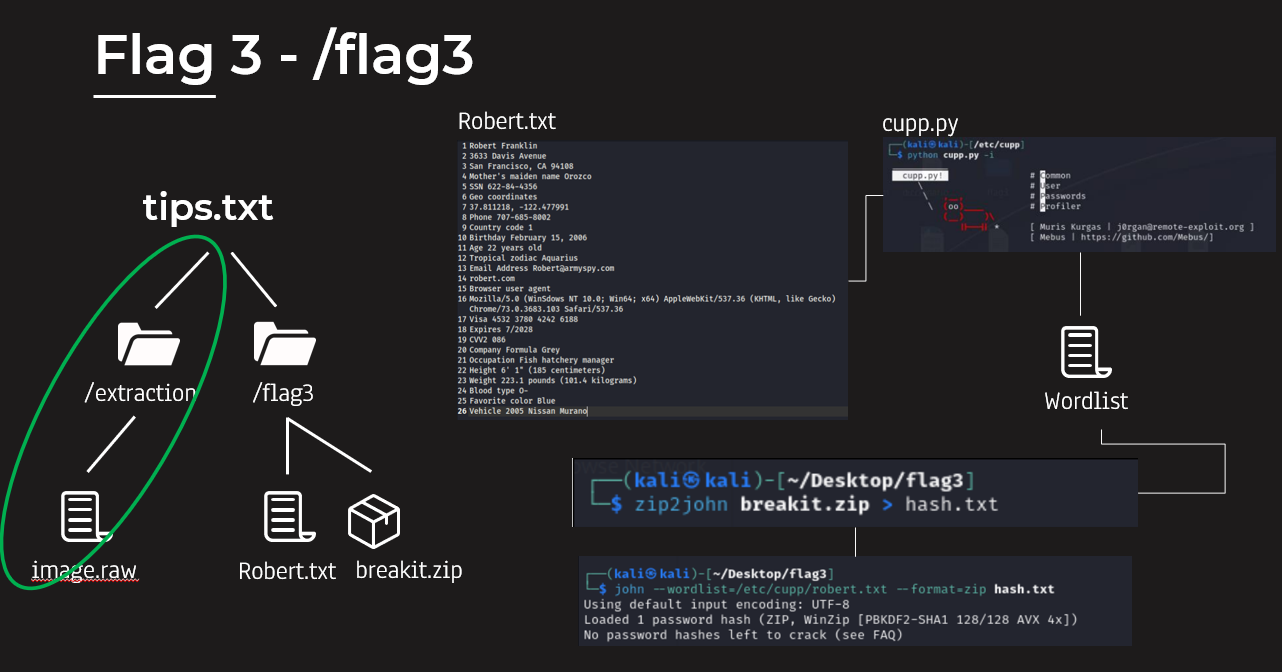
Wordlist creation, password zip bruteforcing, decrypting chrome password files
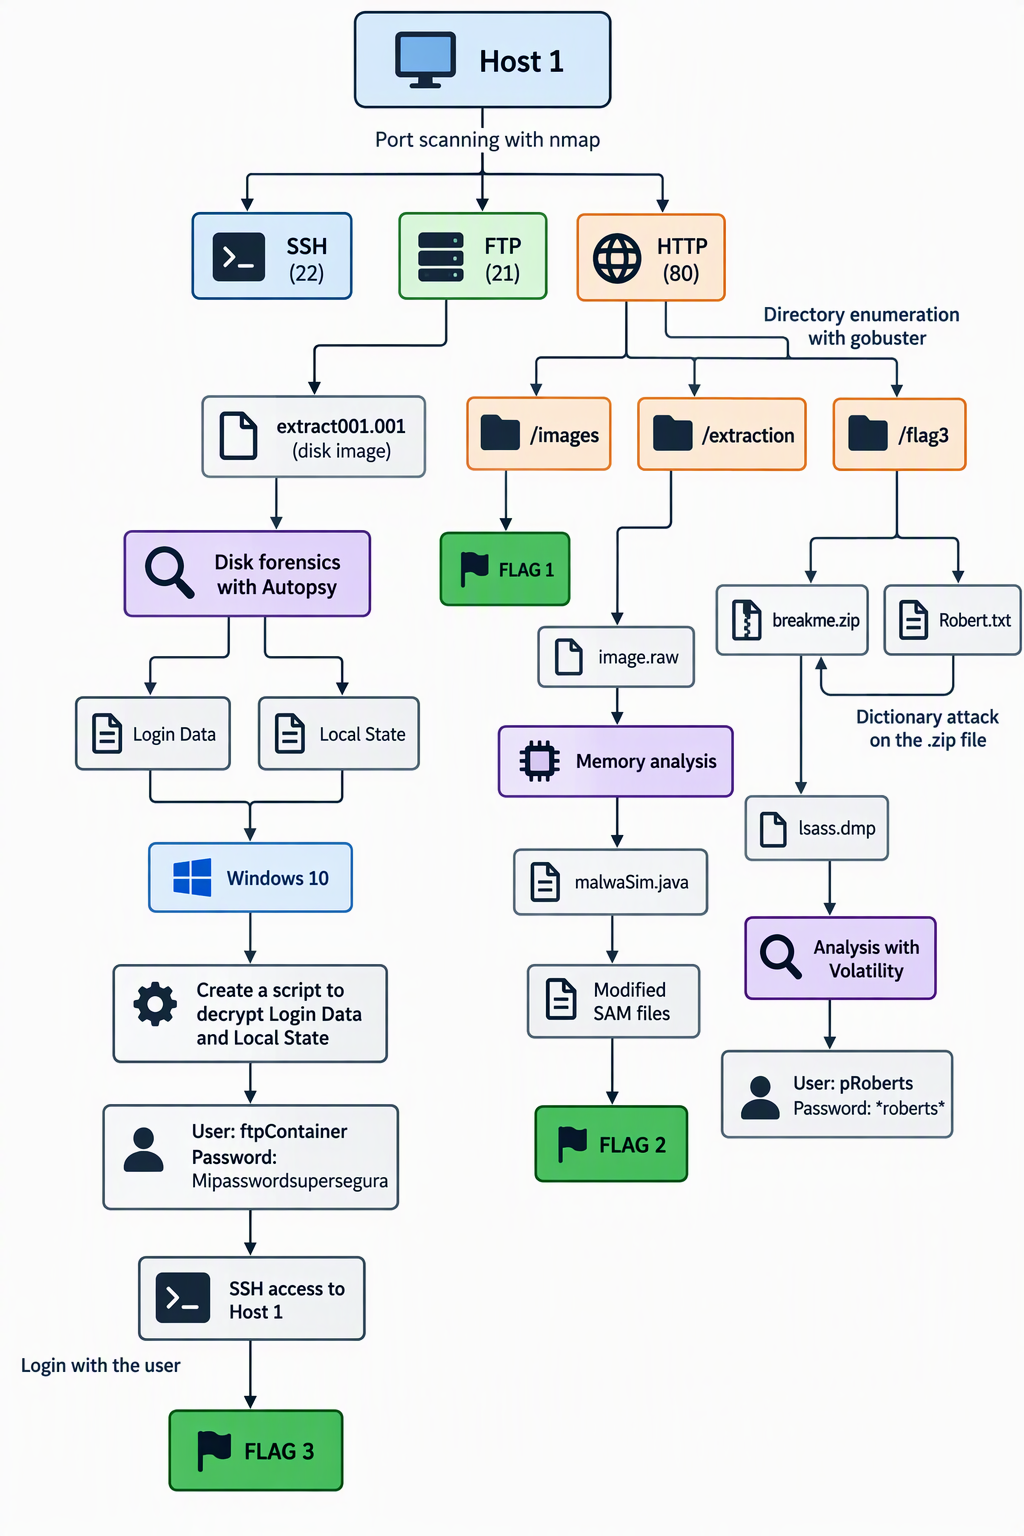
This is a visual walkthrough for solving the lab
Would you be able to solve the BOX? Are you able to find all the flags?
Would you like to check the walkthrough?
Do you have any questions about it?
Feel Free to contact me at any time
Let’s talk security
Open to pentesting and red team opportunities. Available to relocation